Research
responsible disclosureSecurity vulnerabilities found and responsibly disclosed. All findings were reported to the relevant vendor or programme before publication, following coordinated disclosure best practice.
Identified a vulnerability in Singapore's national digital identity platform, used by ~4 million citizens. Reported to the Cyber Security Agency of Singapore (CSA) through responsible disclosure. Acknowledged and patched.
View evidence
Frida trace script and logcat confirming unvalidated deep link URI on sg.ndi.sp v26.1.1.
Java.perform(function() {
  var DeepLinkActivity = Java.use("sg.ndi.activity.DeepLinkDashBoardActivity");

  DeepLinkActivity.onNewIntent.implementation = function(intent) {
    console.log("[VDP-TRACE] DeepLinkDashBoardActivity received a new Intent!");

    if (intent !== null) {
      var dataUri = intent.getData();
      if (dataUri !== null) {
        console.log("[VDP-TRACE] UNTRUSTED INPUT DETECTED: " + dataUri.toString());
        console.log("[VDP-TRACE] WARNING: This string is being passed to internal " +
                    "components without validation.");
      }
    }
    this.onNewIntent(intent);
  };
});08-05 19:53:23.700 F DEBUG : Cmdline: /apex/com.android.art/bin/dex2oat32
--zip-location=.../sg.ndi.sp-w5miu1jf_g6hQR2y2xwZyg==/base.apk
--comments=app-name:sg.ndi.sp,app-version-name:26.1.1,app-version-code:200
...
[VDP-TRACE] DeepLinkDashBoardActivity received a new Intent!
[VDP-TRACE] UNTRUSTED INPUT DETECTED: singpass://dashboard?redirect=...
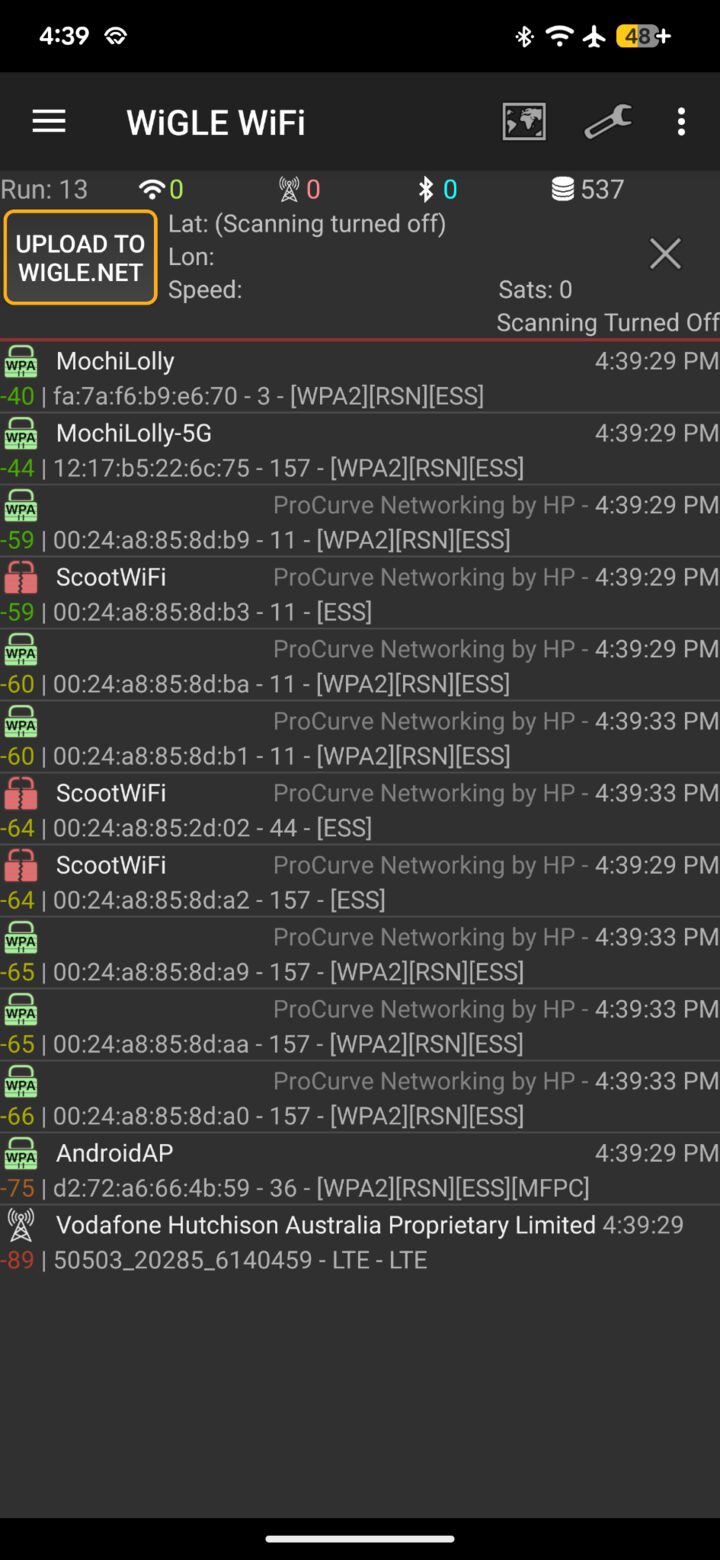
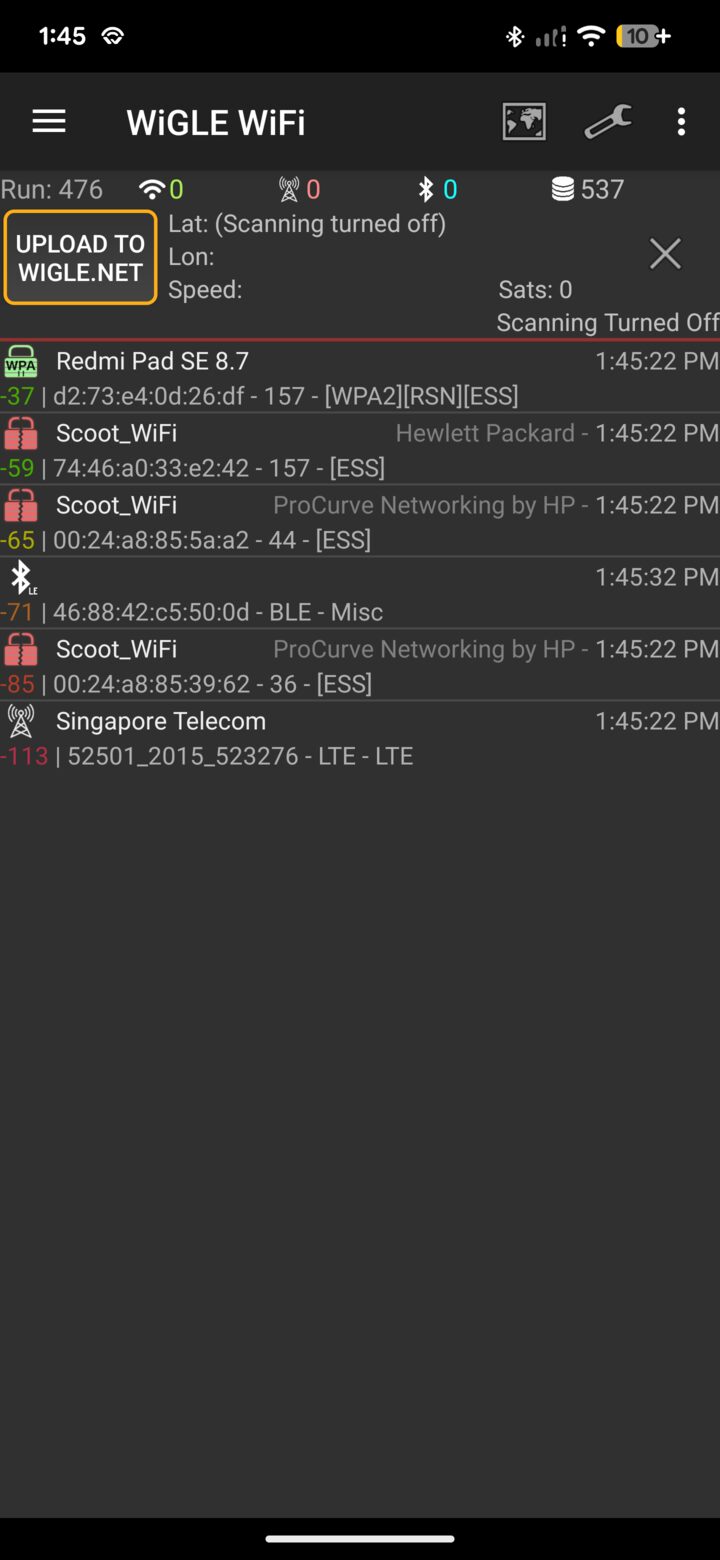
[VDP-TRACE] WARNING: This string is being passed to internal components without validation.Confirmed network segmentation failure on two Scoot Airlines 787 flights (TR11 SYD→SIN and TR14 SIN→SYD, June 2026): ICMP echo requests from the passenger WiFi received replies from internal aircraft IP addresses, violating DO-326A/ED-12C airworthiness security isolation requirements. HP ProCurve hardware confirmed via WiGLE passive scanning (BSSIDs 00:24:a8:xx:xx:xx). Theoretical attack surface includes lateral movement to operational networks (est. CVSS 9.5) and cross-domain protocol injection into ARINC 429/AFDX (est. CVSS 10.0). No exploitation attempted. Disclosed to Boeing PSIRT, FAA, CAAS Singapore, SingCERT, CERT/CC and ASD.
View evidence
WiGLE passive WiFi scans confirming HP ProCurve hardware on both flights, June 2026.
Research into the security model and hardening surface of GrapheneOS, a privacy and security-focused Android distribution. Findings reported to the GrapheneOS security team.
View evidence
Research scope and methodology.
Analysis focused on the GrapheneOS hardening surface: SELinux policy gaps, app sandbox escape vectors, and permission model edge cases specific to the GrapheneOS fork versus AOSP. Research conducted on a Pixel device running GrapheneOS. Findings reported directly to the GrapheneOS security team via their published disclosure channel. Technical details withheld pending full remediation confirmation.
PushDeepLinkActivity is exported and reachable without authentication via ADB or a malicious app, risking denial of service or logic abuse.
View evidence
Vulnerable manifest entry — PushDeepLinkActivity exported with no permission gate.
<!-- AndroidManifest.xml — Lotus app 1.2.8 -->
<activity
  android:name="com.lotus.app.PushDeepLinkActivity"
  android:exported="true" />
<!-- No android:permission attribute. Any caller, any URI. -->allowBackup=true in the manifest allows full user data to be extracted over ADB backup on rooted or debug-enabled devices.
View evidence
Vulnerable manifest entry — allowBackup not disabled.
<!-- AndroidManifest.xml — Lotus app 1.2.8 -->
<application
  android:allowBackup="true"
  ... >
<!-- Full app data extractable via: adb backup -apk -nosystem com.lotus.app -->
"After everything there was the after party where I was able to meet and chat with some super sick people especially Jack Sessions (he pwned Singpass btw). Bro is literally the embodiment of 'living on the edge' whilst being the sickest person ever."
Koh Tom Han, Wannabe Vulnerability Researcher · SinCon 2026
"What an asset to have on any ticket! Nice work CeylonCon!"
Victor Hanna, Director & Chief Hacking Officer · Exploit Security · on the CeylonCon Ambassador announcement
Ambassador
Jack Sessions
DFIR, UAV & Mobile Security Researcher · Australia
"Integrity and character are the only metrics that outlast every other measure of success in cybersecurity."
CeylonCon is Sri Lanka's annual community-driven technology conference, run by the Ceylon Computer Foundation. Jack was announced as the Australian ambassador: representing the CeylonCon community across Australia and the Sri Lankan diaspora, and connecting the security research communities of both countries.
Tools
Four open-source security tools on PyPI. See all on PyPI ↗
pipx install hayabusa-lensPhantomTraceRead-only NTFS integrity checker: MFT vs cluster bitmap vs run listspipx install phantom-trace-ntfsmanifest-traceBatch-scans Android APKs for exposed components, backup flags, cleartext issuespip install manifest-traceruntime-traceeBPF-based Linux runtime checker for process hiding and fileless executionpip install runtime-traceOther Research
Ongoing and forthcoming research areas. Write-ups in progress.
Research into EMP-generating devices, hardening techniques for embedded systems against electromagnetic pulse attack, and the intersection of physical disruption tools with digital forensics and electronic evidence.
More detail
Focus areas: EMP pulse characteristics and shielding thresholds for embedded systems (Faraday cage construction, TVS diode placement, ferrite core selection); how flash-bang and EMP devices interact with digital evidence preservation in first-responder and DFIR contexts; and whether physical disruption events leave artefacts recoverable under NIST SP 800-101 mobile forensic guidelines. Write-up in progress.
UAV-mounted signals intelligence: passive RF collection, spectrum analysis from airborne platforms, and the security posture of civilian drone communication links (MAVLink, DJI OcuSync, custom RF stacks).
More detail
Active work: passive spectrum capture from a small UAV platform (SDR + Raspberry Pi); analysis of MAVLink v2 authentication gaps (unauthenticated heartbeat injection); and DJI OcuSync 2.0 link characterisation. Secondary angle: SIGINT drone detection — what RF signatures a passive collector leaves, and whether standard IDS tooling (Kismet, rtl_433) catches it at range. Write-up in progress.
Design and analysis of hardware and software dead man switch systems intended to trigger data destruction or encryption on device seizure. Research covers both implementation (for understanding defensive use cases) and forensic bypass techniques.
More detail
Research covers three implementation classes: (1) USB kill-switch dongles that trigger LUKS key wipe on removal; (2) network heartbeat systems that encrypt or destroy data if a keepalive beacon stops; (3) hardware tamper sensors (accelerometer/light sensor triggered). Forensic bypass research focuses on imaging before the switch fires — power analysis, cold-boot attacks, and write-blocker strategies. Both offensive and defensive analysis; no exploitation of live systems.
Vulnerability research on networked consumer appliances: attack surface mapping, firmware extraction, exposed network services, and weak authentication patterns in smart home devices.
More detail
Target: a networked smart fridge with a companion Android app and cloud API. Attack surface: firmware (binwalk extraction, hardcoded credentials check), exposed local network services (nmap, Shodan for similar models), companion app (manifest-trace, Frida), and cloud API (Burp, auth token analysis). Goal: a full attack chain from LAN access to account takeover or data exposure. Vendor notified if anything material is found before publication.
Exploitation research on the Sony PlayStation Portable: bootloader vulnerabilities, custom firmware analysis, Memory Stick attack surfaces, and using retro hardware as a platform for learning kernel-level exploitation primitives.
More detail
The PSP is a contained MIPS platform with well-documented but historically under-explained exploits. Research goals: reproduce the original HEN/CFW exploit chains from first principles (no patched binaries), understand the Memory Stick format parser attack surface, and use the PSP as a clean environment for practising kernel heap and stack exploitation without the noise of modern mitigations (ASLR, NX, CFI). Write-up aimed at other researchers wanting a hardware exploitation primer.
Talks
Research presented at BSides Tokyo, BSides Canberra, SinCon Singapore, AVTOKYO and more. Full list →
Want to work together?
Open to security research roles, consulting engagements, and speaking invitations. Mobile, DFIR, aviation/UAV, AI safety. Pick one and it opens an email.