About
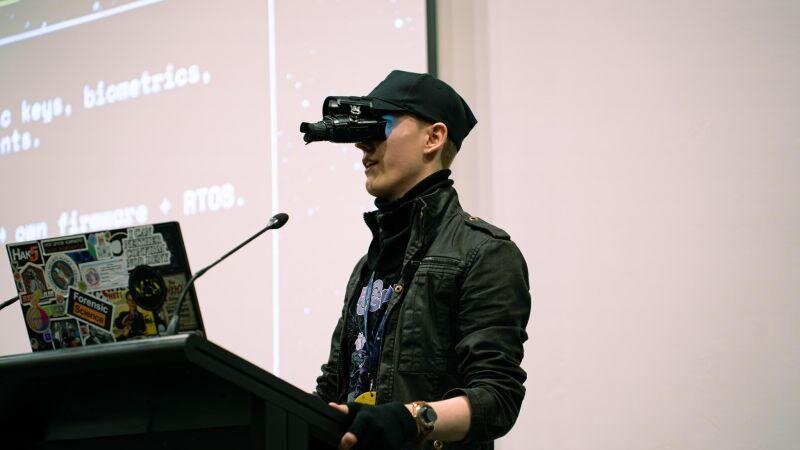
I'm Jack Sessions — security researcher specialising in mobile security, DFIR, and vulnerability research. I've found and responsibly disclosed security issues to the Cyber Security Agency of Singapore, Boeing PSIRT, the FAA, and Australia's ASD, among others. I hold a GCFA, speak at international security conferences across Asia-Pacific and Europe, and build open-source DFIR tooling used by practitioners. Currently studying Computer Science at UNSW.
Security Researcher (Mobile). Bounty hunter for the US Diplomatic Security Service, helping 12 countries' security services find and track cyber criminals. Contributes to many open source projects with a focus on mobile security and AppSec. Works on phone and device security, particularly anti-forensics and counter intelligence.
What I work on
Mobile security
Android APK analysis, iOS bootchain and Secure Enclave research, and runtime instrumentation.
Anti-forensics & counterintelligence
How devices and people hide, spoof and mislead, and how investigators see through it.
DFIR
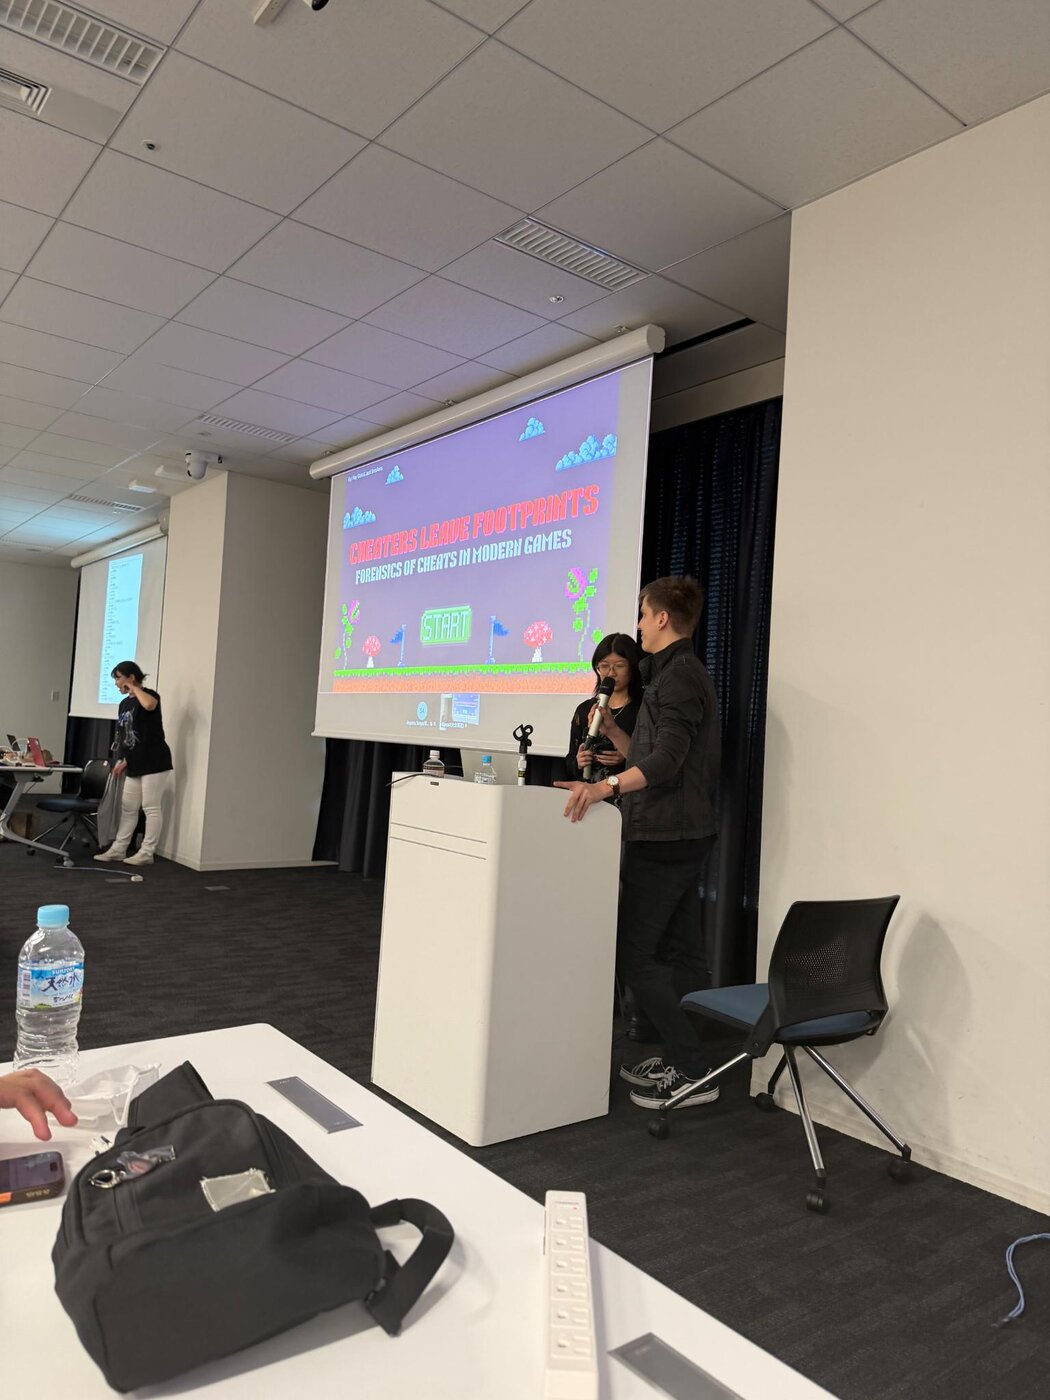
Memory, disk and telemetry forensics, including how game cheats leave footprints.
UAV & aviation security
Network segmentation in aviation systems, DO-326A/ED-12C compliance, and UAV communication security research.
Crypto investigations
Tracing funds and building evidence trails for cases that cross borders.
Published tools
Four open-source security tools on PyPI. All packages ↗
Hayabusa Lens
A dashboard for Hayabusa and Chainsaw with a 3D attack map and an AI investigator that keeps an audit trail of every question it asks.
pipx install hayabusa-lensPhantomTrace
A read-only NTFS checker that compares the MFT, cluster bitmap and run lists and flags where they disagree, a possible sign of tampering.
pipx install phantom-trace-ntfsmanifest-trace
Batch-scans Android APK manifests for exposed components, backup flags, debuggable flags, and cleartext traffic issues. Fast triage for mobile pentesters.
pip install manifest-traceruntime-trace
Linux runtime consistency checker using eBPF to detect process and module hiding and fileless execution. Built for DFIR and blue teams.
pip install runtime-traceTech stack
Research & recognition
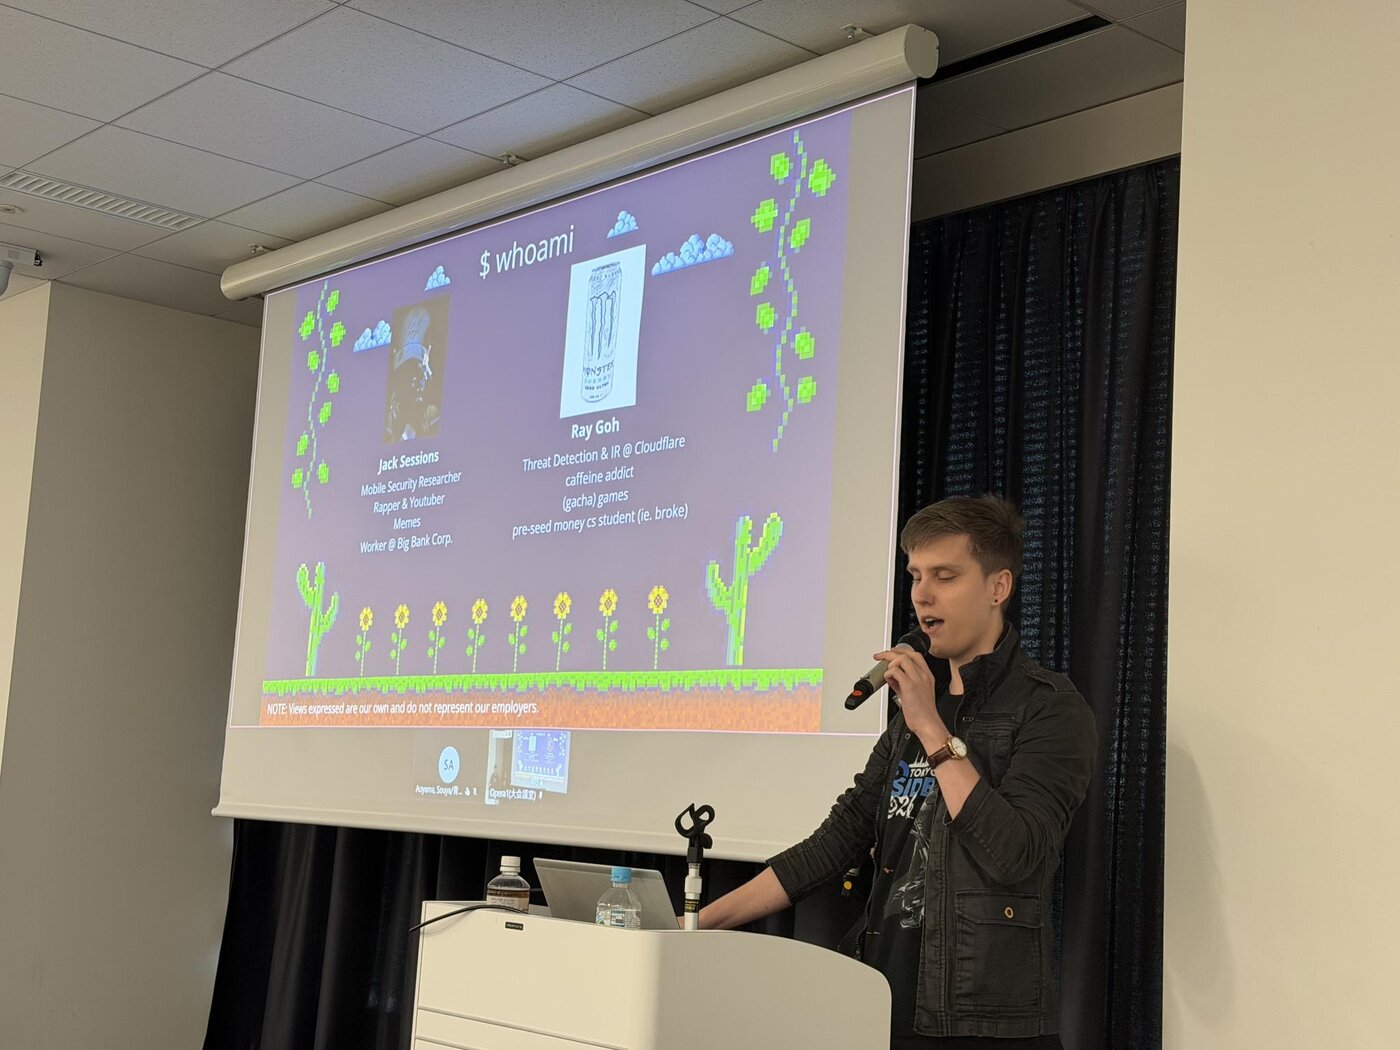
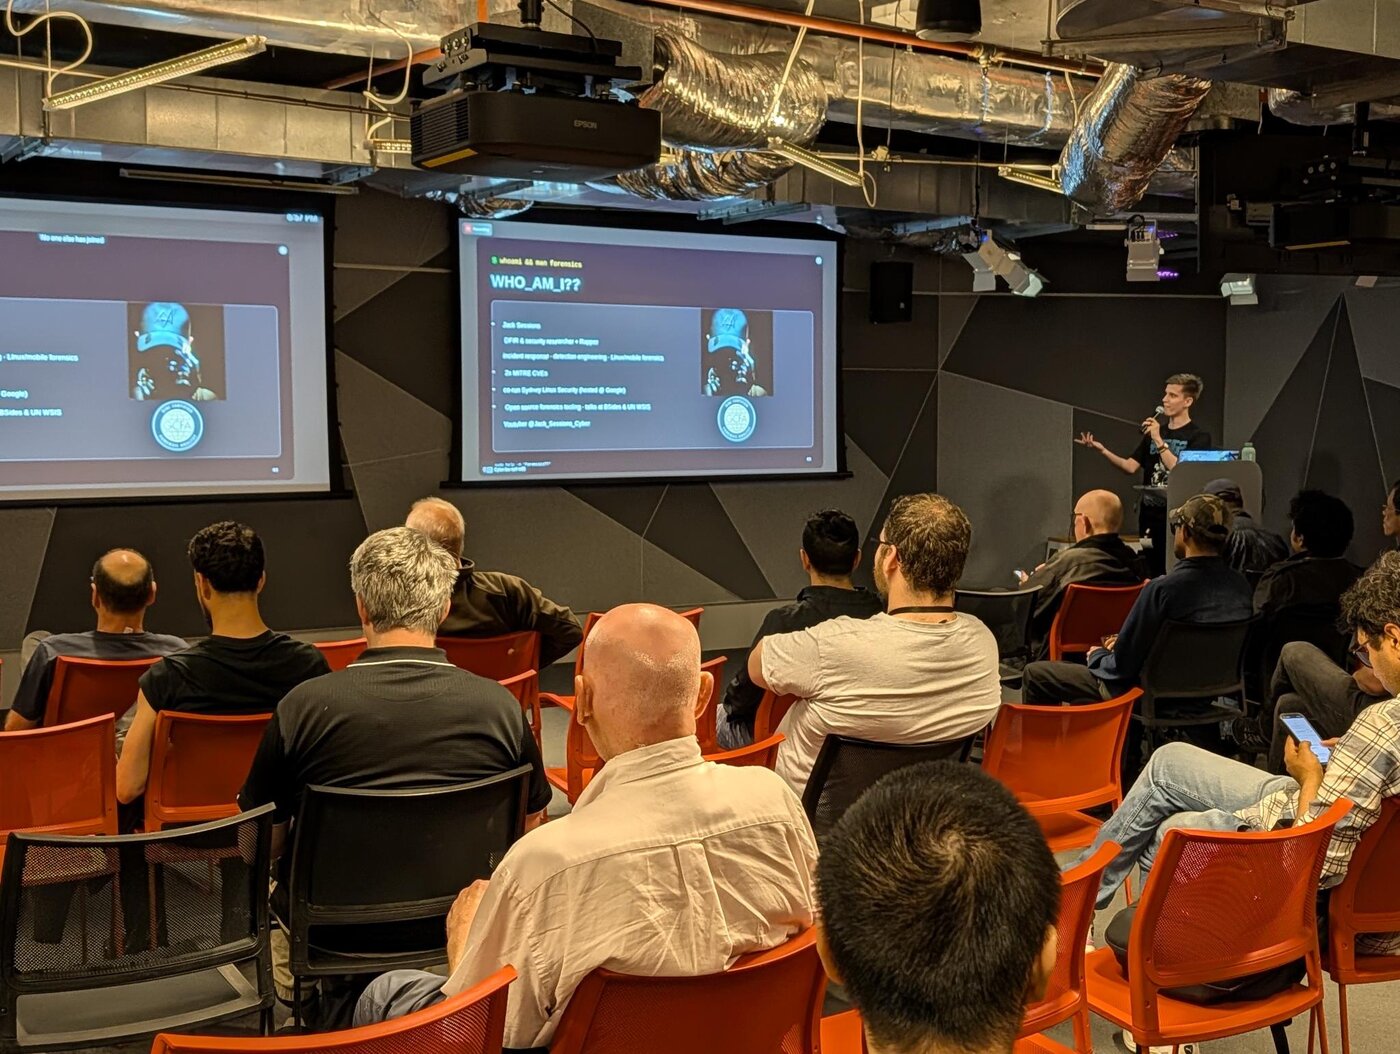
More research is presented on the talks page, with slides for most sessions.
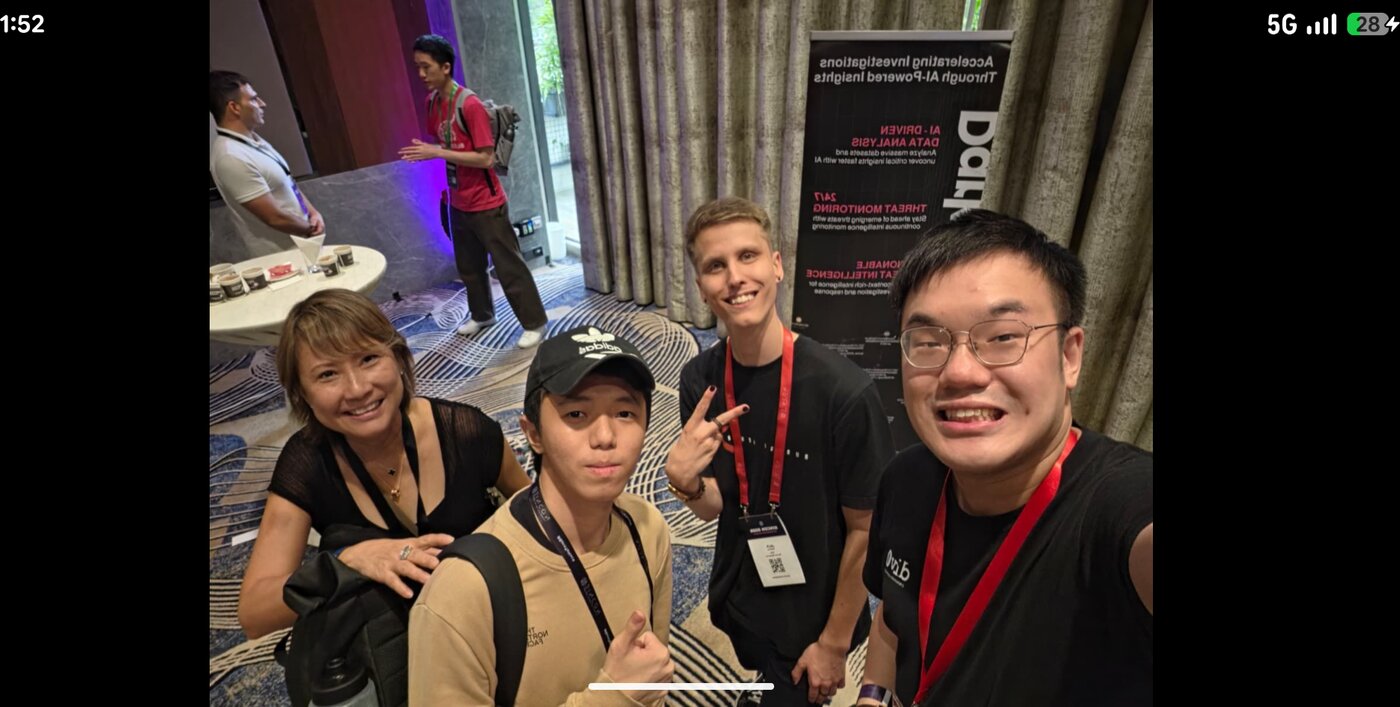
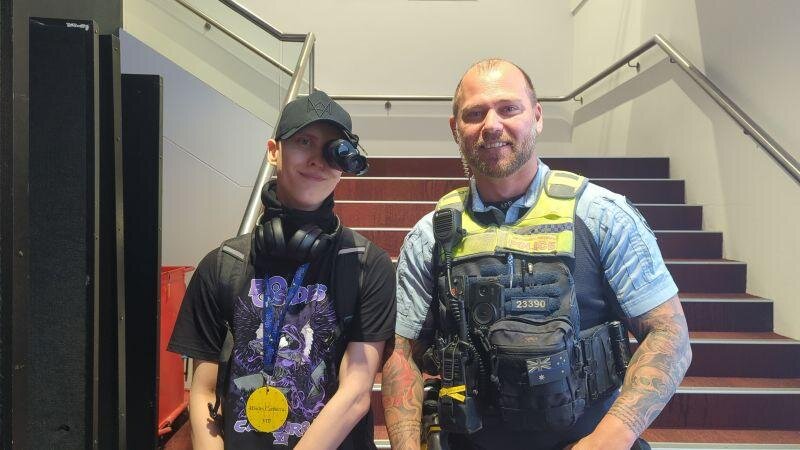
Photo reel
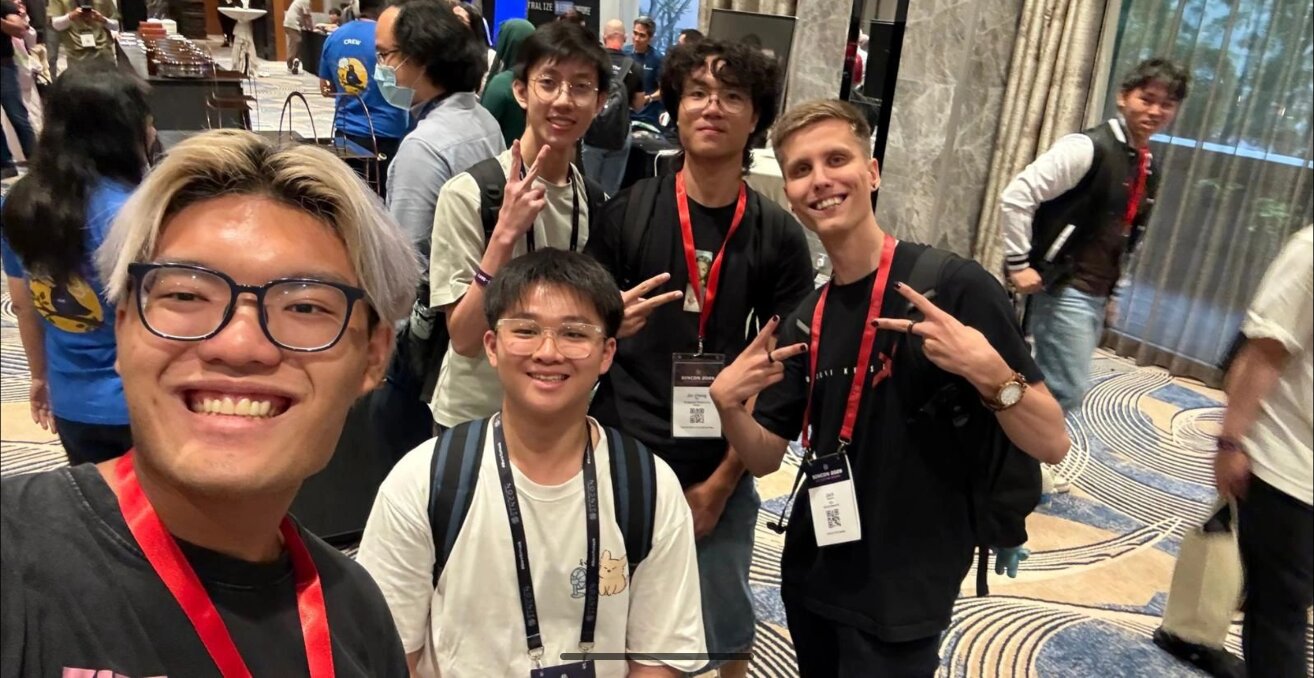
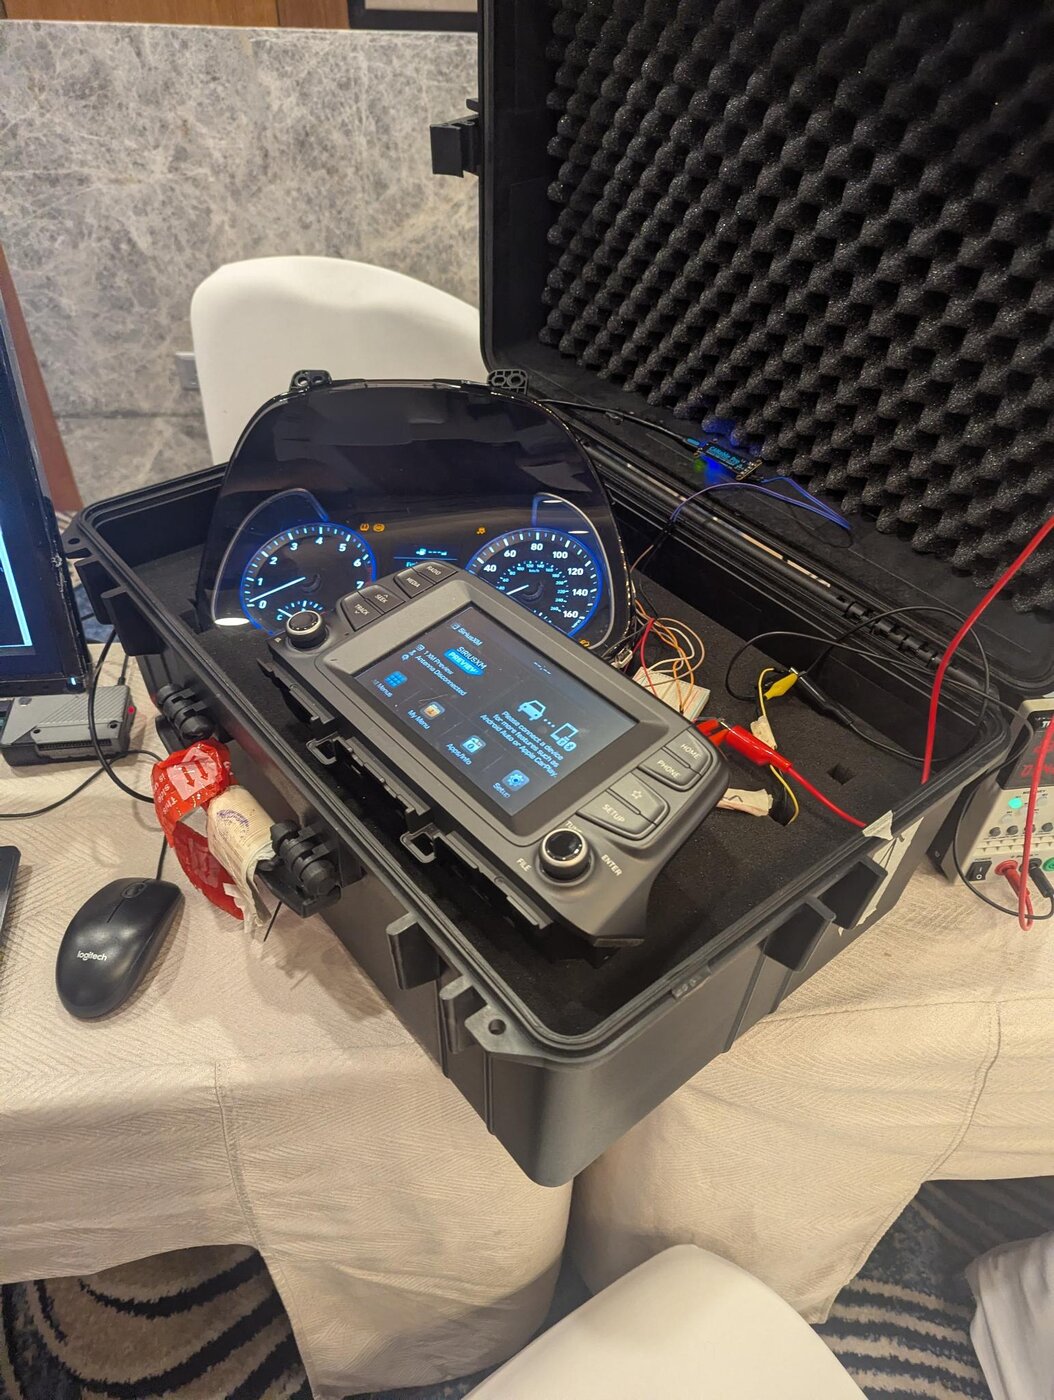
Off the clock
🎵 Soundtrack for deep work
Jeremy Soule's Oblivion and Skyrim OSTs are basically a second brain. Auriel's Ascension for architecture decisions, Call of Magic for late-night reversing sessions. Criminally underrated focus fuel.
🐱 Cat volunteering
I volunteer at a local cat shelter on weekends. Turns out socialising rescue cats and debugging kernel panics require the same energy: patience, snacks, and refusing to give up.
🎤 Rap & music production
I write and record my own tracks. Security researcher by day, emcee by night. There's more overlap than you'd think — both involve pattern recognition and knowing when to go hard.
✈️ Conference travel
BSides Tokyo, SinCon Singapore, AVTOKYO — half security research, half excuse to eat good food and find the best local coffee. Currently chasing talks on five continents.
Recognition
Official community representative for CeylonCon — Sri Lanka's annual technology conference run by the Ceylon Computer Foundation. Bridging the security research communities of Australia and Sri Lanka.
Certifications
 GCFA
GIAC Certified Forensic Analyst BTL1
Blue Team Level 1 Security+
CompTIA Security+
Working toward GEIR. Verify on Credly.
Education
UNSW, Bachelor of Computer Science (expected 2028)
Want to work together?
Open to security research roles, consulting engagements, and speaking invitations. Mobile, DFIR, aviation/UAV, AI safety. Pick one and it opens an email.